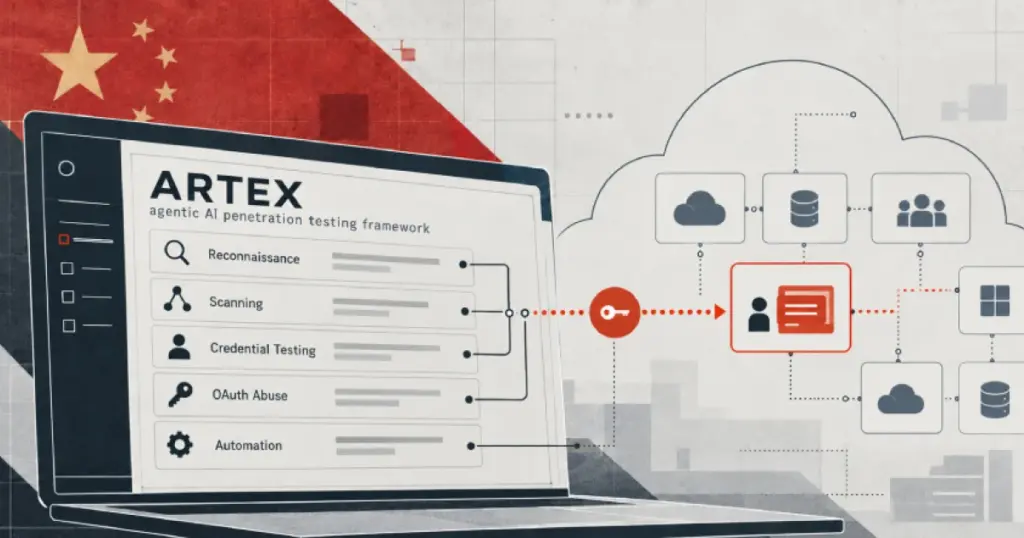
- China state-aligned actor Storm-0940 utilized ARTEX AI agents in a supply chain attack targeting ConnectWise Cloud Backup.
- The breach affected over 2,250 Microsoft 365 tenants, with hackers gaining privileged access in under three hours.
- ARTEX is a Go-based AI penetration testing framework that automated scanning, password spraying, and exploitation.
Microsoft has disclosed that Storm-0940, a China state-aligned actor active since at least 2021, was responsible for the recent supply chain compromise of the ConnectWise Cloud Backup application. The attackers leveraged AI agents to accelerate and scale their operations, targeting over 2,250 Microsoft 365 tenants.
The Deployment of ARTEX AI Agents
During the incident, Storm-0940 employed ARTEX, a Go-based agentic AI penetration testing framework. This tool, which was made closed-source following its abuse against South Korean financial institutions, automates reconnaissance, vulnerability discovery, credential attacks, and data theft. Microsoft emphasized that ARTEX enables attackers to operate around the clock with minimal human interaction, significantly reducing the detection and response window for defenders. Storm-0940 began utilizing ARTEX as early as September to target organizations globally, including government agencies, defense contractors, banks, manufacturers, and tech firms.
Attack Timeline and Scope
Between October 10 and 14, the hackers initiated over 151,000 failed sign-in attempts against 327 accounts at eight organizations through password spraying. While no successful logins were observed from this campaign, the attackers subsequently shifted to compromised ConnectWise application identities. These compromised credentials allowed them to exploit permissions customers had already granted to ConnectWise services, bypassing the need for interactive user logins.
Armed with ARTEX, Storm-0940 attempted to authenticate against more than 2,250 Microsoft 365 tenants, at times reaching 2,900 attempts per minute. Microsoft also observed AI-accelerated activity through Microsoft Graph, including reconnaissance, application credential changes, and attempts to modify privileges, potentially allowing the attackers to maintain persistence even after original credentials were revoked.
Although most attempts failed, Microsoft confirmed that the hackers successfully established persistent privileged access at numerous organizations. The exact number of compromised customers or whether data was exfiltrated has not been disclosed, as a successful login does not automatically imply data access.
ConnectWise Response and Prior Incidents
ConnectWise, an IT management vendor, responded to the unauthorized access to application identities by taking its Cloud Backup, SaaS Security, and Cloud Management services offline as a precaution. ConnectWise CEO Manny Rivelo stated that the company contained the affected application connections and was gradually restoring services. However, he cautioned that shutting down these connections would not necessarily remove attackers who had already established a foothold in customer environments.
This is not ConnectWise’s first security challenge. In May 2025, the company acknowledged that a “sophisticated nation-state actor” had breached its systems and compromised a small number of customers using its ScreenConnect remote access software. There is no indication that the two attacks are linked. For more context on the broader impact of AI on technology, refer to our article: SK Hynix Predicts Memory Shortages to Persist Until 2030 Amid Soaring AI Demand.
Wider Adoption of ARTEX
Microsoft noted that Storm-0940 is not alone in utilizing ARTEX. The framework, which is freely available for penetration testing, has been observed in use by threat actors from several geographic regions. While the underlying techniques-stolen credentials, password spraying, and application abuse-are not novel, AI significantly enhanced Storm-0940’s execution speed, with some attacks progressing from initial targeting to privileged cloud access in under three hours.
| Parameter | Details |
|---|---|
| Attacking Group | Storm-0940 (China-aligned) |
| Tool Used | ARTEX (AI Penetration Testing Framework) |
| M365 Tenants Affected | Over 2,250 |
| Time to Privileged Access | Under 3 hours |
| Peak Sign-in Attempts | 2,900 attempts/min |
| Target Industries | Gov. agencies, defense contractors, banks, manufacturers, tech firms |
| ConnectWise Disclosure Date | October 16 |
| Microsoft Disclosure Date | October 21 |
This incident underscores the escalating threat posed by cyberattacks that leverage AI to automate and accelerate operations. For organizations, this necessitates reinforcing multi-factor authentication, regularly auditing application permissions, and proactively monitoring for suspicious activity. Service providers like ConnectWise must prioritize supply chain security, as a compromise in one link can jeopardize thousands of customers. The deployment of AI agents like ARTEX reduces the defender’s reaction time, demanding more advanced and automated threat detection systems.
This ARTEX news is unsettling, especially since I’ve been experimenting with similar open-source AI frameworks for red teaming exercises internally. The speed at which these AI agents operate is truly a game-changer; they can automate so many mundane recon tasks, saving hours. However, I’ve found that custom module integration can still be a bit clunky, requiring manual oversight to avoid false positives or unnecessary noise. My tip: always have a human ‘kill switch’ and validate initial findings to prevent runaway automation from flagging benign activity as malicious, or worse, causing unintended disruption.