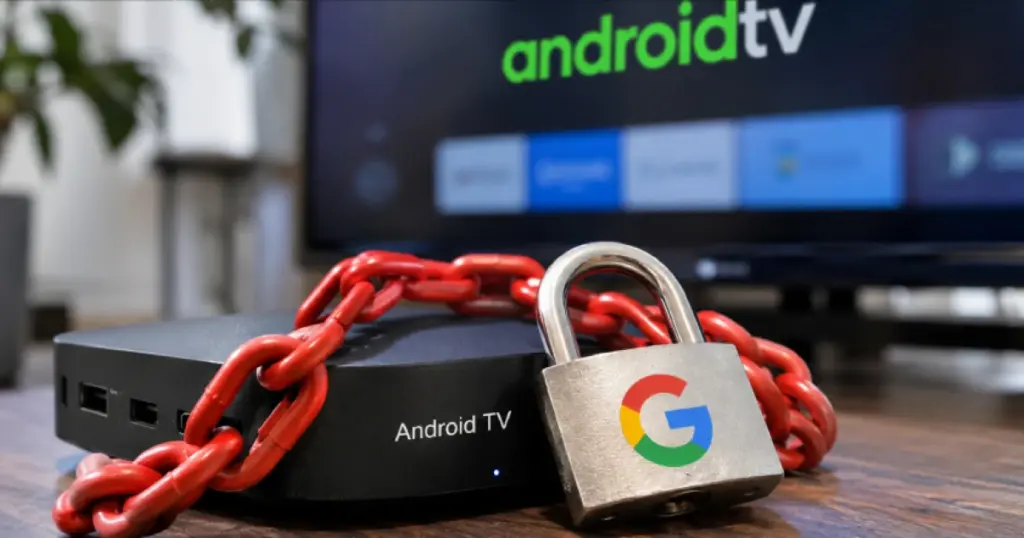
- Google, in collaboration with law enforcement and private security firms, has dismantled a botnet comprising over 1.3 million Android devices.
- The device manufacturer, Videostrong Technology Co., intentionally embedded the XCPE backdoor in firmware and sold access to criminals.
- The botnet was utilized for ad fraud and routing malicious traffic through unsuspecting users’ internet connections across more than 200 countries.
Major Takedown of the XCPE Android Botnet
Google, in conjunction with a coalition of private-sector security firms including Lumen, Human Security, Plume, Synthient, and TrendAI, and with the support of Japan’s National Police Agency, has successfully disrupted the XCPE botnet. This network consisted of over 1.3 million Android devices, predominantly TV set-top boxes, spanning more than 200 countries. The command-and-control servers for this botnet were taken offline in late October.
Videostrong Technology Co. Implicated
The Google Threat Intelligence Group (GTIG) states with high confidence that Shenzhen, China-based hardware manufacturer Videostrong Technology Co. deliberately embedded the XCPE backdoor into the firmware of its Android devices, including home TV boxes and projectors. Access to this backdoor was then sold to criminal affiliates, enabling them to install additional malware modules on devices shipped to unsuspecting customers. When these devices were connected to home networks, the preinstalled backdoor allowed operators to establish proxy networks and conceal malicious traffic using the customers’ internet connections without their knowledge.
How the Backdoor Operated
According to TrendAI, the firmware’s pre-installed management agent masqueraded as a standard remote-management client. It fetched updates from a GitHub page and connected to a Message Queuing Telemetry Transport (MQTT) server, which granted the operator full remote control over each box. This capability allowed for the installation and removal of applications, modification of settings, and pushing updates to the infected devices. Between June 3 and October 1, TrendAI documented over 3.8 million distinct home and mobile IP addresses connected to this operation.
Consequences and Future Actions
The coalition also disrupted the command-and-control (C2) domains used to manage the affiliate modules. GTIG assesses that this action will sever access to at least 10 million additional compromised devices, as these affiliates possess diversified distribution channels for their modules beyond XCPE. Google has since confirmed cutting ties with Videostrong and has banned the OEM from manufacturing devices with preloaded Google apps.
This backdoor and botnet operation is part of the same ecosystem as BadBox 2.0, another notorious botnet that infected over 10 million TV boxes and other devices before Human, Google, and TrendAI disrupted it in March 2023. For more insights into widespread cyberattacks, you might find our article Second Wave of Cyberattacks Cripples European Supermarket Freezers, Destroying Millions in Food Stocks relevant.
This incident underscores the critical importance of vigilance when purchasing devices from lesser-known manufacturers, especially those offering unusually low prices. Consumers should be wary of devices that request excessive permissions or exhibit suspicious network activity. For the industry, it signifies a heightened need for stringent oversight and certification by platforms like Google to prevent pre-installation of malicious software at the hardware level. This will ultimately lead to enhanced security for the entire Android ecosystem.
The intentional embedding of the XCPE backdoor by Videostrong Technology Co. into firmware, particularly in Android TV boxes, highlights a critical supply chain vulnerability. This operation, leveraging MQTT for C2, allowed for sophisticated ad fraud and traffic proxying, demonstrating a deliberate monetization strategy from the OEM level. The estimated 10 million additional compromised devices through diversified affiliate channels underscores the pervasive nature of such pre-installed malware and the complexity of remediation beyond a single botnet takedown.