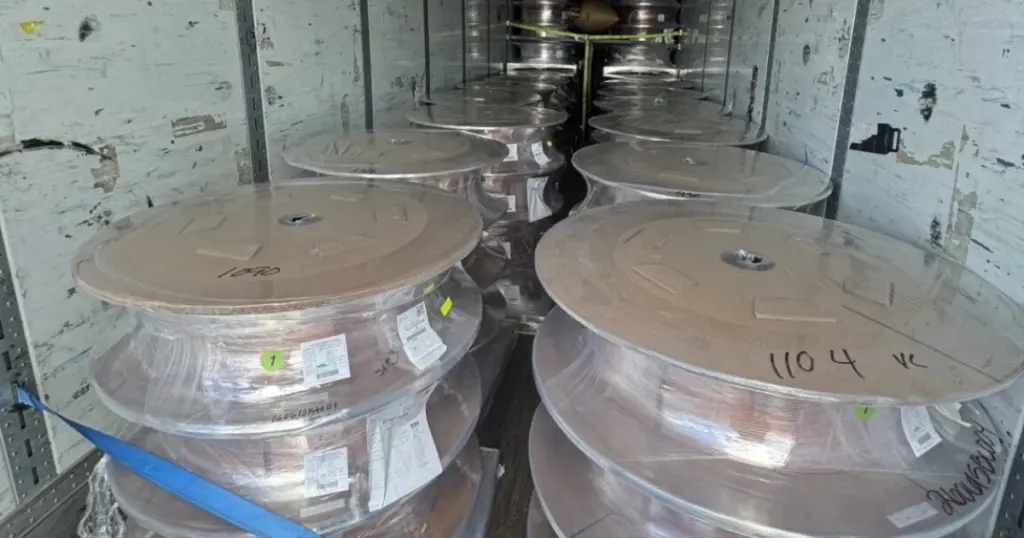
- Organized crime groups have stolen over $100 million in data center equipment since June of this year.
- Thieves employ a blend of cyber tactics (phishing, freight broker account hacking) and physical violence (ramming escort vehicles), alongside GPS spoofing to evade tracking.
- The stolen high-value gear, including servers, RAM, and cabling, is often pre-sold to international buyers, some in countries under strict U.S. AI export controls.
Sophisticated Heists Target Data Center Equipment in Transit
Organized crime groups have stolen over $100 million in data center freight since June of this year, according to an NBC News report. These incidents highlight a worrying trend where thieves are using a combination of sophisticated digital tactics and physical force to intercept valuable cargo.
The Modus Operandi: From Phishing to GPS Spoofing
The elaborate schemes begin with thieves hacking into freight brokers’ accounts on shipment-listing websites. They post fake shipments to attract legitimate bids, then send malicious links to responding trucking companies. Once clicked, this software allows the criminals to take control of the victims’ accounts and bid on real shipments.
Sometimes, a genuine delivery driver is unwittingly hired to collect the cargo. In other instances, fake driver’s licenses are used to get accomplices hired. The goods are eventually transferred to a driver working with the thieves for resale. In one of the largest thefts, GPS tracking coordinates were spoofed to prevent digital monitoring, making it appear as though the cargo was still on its intended route.
High-Value Targets and Escalating Losses
The stolen gear includes servers, fiber-optic and copper cabling, RAM modules, storage drives, routers, and other miscellaneous components crucial for building AI data centers. One incident in Reno resulted in $38 million in gear disappearing. In July 2025, $15 million worth of semiconductors and Apple products were nabbed in the same city. June 2026 saw $13 million in gear stolen around the Mojave Desert area and $10 million worth of server rack components headed for Texas.
Even copper wire is a valuable target; one snagged trailer held $300,000 worth of the metal. Keith Lewis from Verisk Cargonet states, “It’s like stealing pure gold bars […] it’s so much easier to steal [data center shipments] than to rob a bank.”
| Equipment Type | Estimated Value | Incident Location |
|---|---|---|
| Server Equipment | $38 million | Reno |
| Semiconductors & Apple Products | $15 million | Reno |
| Server Equipment | $13 million | Mojave Desert Area |
| Server Rack Components | $10 million | En route to Texas |
| Copper Wire | $300,000 | Undisclosed |
International Networks and Violent Tactics
Beyond cyber-enabled theft, these heists increasingly involve physical violence. In several recent cases, thieves literally rammed escort cars to ensure a trouble-free getaway for the truck. Law enforcement officials view these as potential escalations of violent tactics more commonly seen in other countries.
Scott Cornell, chair of TAPA Americas, emphasizes that these are “extremely high-level organized rings that are operating from a dozen different countries, targeting freight in the United States supply chain.” He estimates that six to seven out of 10 stolen cargo shipments end up overseas, often to entities in countries under U.S. AI export controls, such as China. Verified Carrier has observed suspicious activity linked to U.S. cargo theft in India, Uzbekistan, Pakistan, Colombia, and Moldova this year.
The FBI issued a warning in April about “cyber-enabled strategic cargo theft,” detailing methods where spoofed broker email addresses are used to gain access to cargo systems and bid on loads, which are then transferred to complicit drivers for resale.
The surge in high-value data center cargo heists necessitates a multi-faceted security approach for logistics providers and data center operators. This includes bolstering cybersecurity measures to protect freight broker accounts, implementing robust driver vetting processes, and enhancing physical security for high-value shipments. The use of GPS spoofing and AI-generated IDs demands advanced tracking technologies and verification systems. Companies must also recognize the international scope of these criminal networks and the pre-arranged nature of overseas buyers, requiring greater intelligence sharing and cross-border cooperation to mitigate risks effectively.
While the article highlights concerning trends in cargo theft, I wonder if focusing solely on GPS spoofing overstates its impact compared to the initial digital infiltration. Hacking freight broker accounts and using malicious links seem to be the primary vulnerabilities. Addressing these foundational cyber security flaws might be more effective than just enhancing GPS resilience, which can always be circumvented by determined criminals using physical force as described.