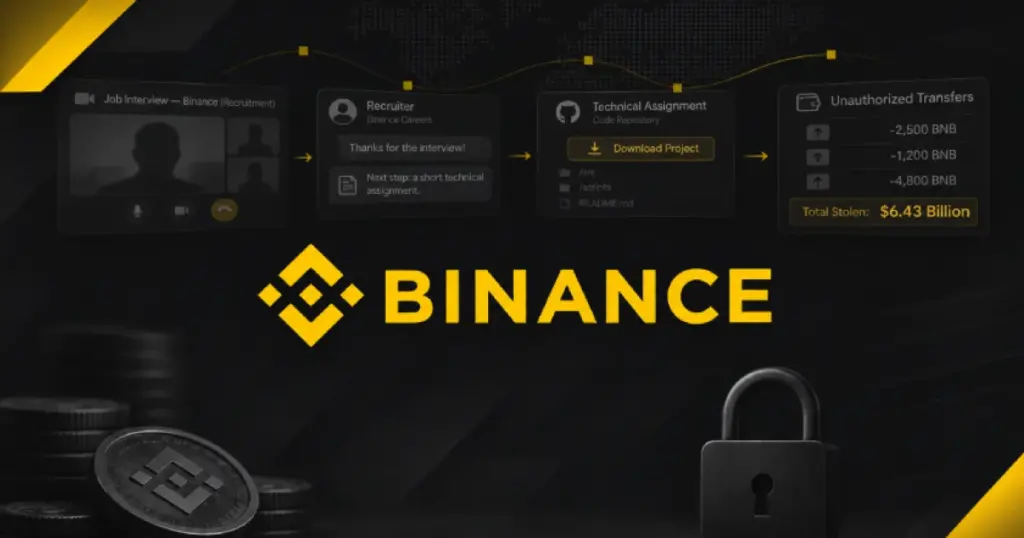
- Binance, the world’s largest cryptocurrency exchange, lost $6.3 billion in a sophisticated cyberattack.
- The attack involved recruitment-themed social engineering, a tampered Homebrew installation, and the exploitation of an internal AI tool.
- Hackers gained access to engineers’ computers over five months before compromising crypto wallets.
Binance Details Sophisticated Multi-Stage Cyberattack Leading to $6.3 Billion Theft
Binance, the world’s leading cryptocurrency exchange, disclosed on Tuesday the intricate details behind the record-setting theft of $6.3 billion in assets. The company characterized the incident as a “sophisticated, multi-stage campaign” rather than a simple phishing incident or an isolated breach.
The process, according to Binance’s postmortem report, began with the compromise of two engineers through a social engineering attack themed around recruitment and the use of a tampered Homebrew installation.
Chronology and Attack Vectors
The cyberattack unfolded over several months, combining known hacking techniques. It initiated when a Wallet DevOps engineer (referred to as Engineer A) downloaded a malicious Homebrew installation, a third-party package manager for macOS. This download was reportedly prompted by a malicious Google ad. While Binance’s security team detected the anomaly, replaced the device, and rotated credentials, the attacker had already exposed details regarding Engineer A’s role and his colleagues within the wallet infrastructure team.
Subsequently, a separate incident involved another software engineer (Engineer B). This engineer was contacted via a legitimate job hunting platform and invited for two rounds of interviews: one with an HR representative and another with a supposed CEO. Both individuals and the company they claimed to represent were fictitious. The purpose of these interviews was to present Engineer B with an ‘assignment’ that was, in fact, a repository of malicious code. This malware executed during setup, running a series of commands and evasion techniques to bypass Binance’s security checks.
Exploiting an Internal AI Tool to Control Wallets
With Engineer B’s computer compromised, the attackers leveraged an internal AI tool at Binance to gain control over two additional machines: Engineer A’s and another Wallet Software engineer’s (Engineer C). On Engineer A’s machine, a container deployment permission token was discovered. Using this token, the hackers logged into Engineer C’s computer with stolen credentials, created a container, and triggered a malicious script. This ultimately enabled them to seize control of the crypto wallets used for storing transitory funds by the exchange, leading to the withdrawal of $6.3 billion.
| Attack Phase | Description | Timeline |
|---|---|---|
| Tampered Homebrew Download | Engineer A downloaded a malicious Homebrew installation via a search engine ad. | June (Approx.) |
| Fake Job Interviews | Engineer B was lured into fake interviews, leading to malware installation. | Over several months |
| Internal AI Tool Exploitation | Hackers used an internal AI tool to access additional machines. | Post-engineer compromise |
| Fund Exfiltration | Control over wallets gained, $6.3 billion stolen. | After 5 months of access |
Over a period of five months, the hackers systematically gained access to employee computers before utilizing an internal AI tool to take command of the exchange’s wallets. This incident marks what is potentially the largest financial theft in cryptocurrency history.
The FBI has previously suggested a North Korean hacking group was behind the attack, an accusation North Korean officials have denied. Binance has successfully frozen approximately half of the stolen funds and has already covered the remaining losses.
This incident raises significant concerns about corporate cybersecurity practices, particularly concerning the integration of AI-powered tools within critical infrastructure environments.
This incident underscores the critical importance of multi-layered security and robust cybersecurity training for all employees. Even advanced security technologies can be circumvented through human factors and social engineering. Companies must enhance controls over third-party software downloads, rigorously vet recruitment processes, and ensure strict isolation of systems with access to critical assets, especially when integrating internal AI tools. The case highlights that the weakest link often remains the human element, necessitating continuous vigilance and adaptation of security protocols.
This report on the Binance heist is concerning. While the details highlight a sophisticated attack, it also raises questions about the robustness of their internal security protocols, especially given the multi-month infiltration. Relying on an internal AI tool that could be leveraged to compromise multiple machines seems like a significant single point of failure. It makes me wonder about the true cost of such advanced internal systems if they can be turned against the company so effectively.