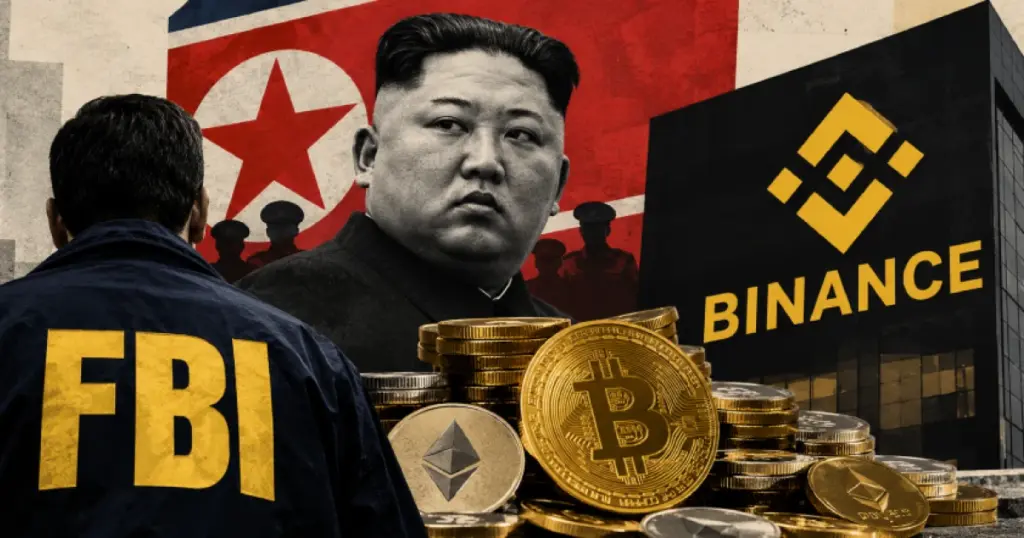
- The U.S. FBI has officially linked the TraderTraitor hacking group, aligned with North Korea, to the theft of over $6 billion in virtual assets from Binance.
- The incident occurred on or about October 29, with hackers converting stolen funds into Ethereum for laundering.
- Binance has reimbursed approximately 95% of the stolen assets but faced significant customer outflows following the attack.
FBI Links North Korea to Massive Binance Crypto Heist
The U.S. Federal Bureau of Investigation (FBI) has officially attributed the theft of more than $6 billion in virtual assets from the Binance cryptocurrency exchange to TraderTraitor, an elite hacking group aligned with North Korea. This group is also tracked under several other names, including Jade Sleet, Pressure Chollima, PUKCHONG, Slow Pisces, and UNC4899, and is associated with the notorious Lazarus Group.
In a statement issued jointly with the U.S. Secret Service (USSS) and the Internal Revenue Service Criminal Investigation (IRS-CI), the FBI confirmed the theft occurred on or about October 29. The agency noted that it has observed actors connected to the hack converting the stolen tokens to Ethereum and preparing for further laundering of the funds.
Attack Details and Binance’s Response
According to the FBI, the hackers have initiated the process of swapping their illicit gains for Ethereum, with investigators anticipating further movement of these funds through decentralized finance (DeFi) platforms and instant swap services to obscure their origin. The agency has released a list of cryptocurrency wallet addresses associated with the theft and urges exchanges, blockchain analytics firms, and other virtual asset providers to block transactions involving these stolen funds.
Binance admitted that hackers had made off with approximately $6.3 billion in cryptocurrency. The breach originated from a compromised DevOps engineer’s laptop, which granted intruders access to a service container and allowed them to authorize unauthorized withdrawals. Following the attack, Binance temporarily suspended customer withdrawals but has since resumed them, reporting that it has replenished about 95 percent of the stolen assets. The remaining tokens are proving more challenging to replace due to their limited liquidity.
Financial Impact and Customer Exodus
The exchange has committed billions of dollars from its own reserves and emergency funds to cover the losses, with co-CEO Richard Teng assuring that customers would not bear the financial burden. Despite these assurances, Binance recorded approximately $3.64 billion in net outflows after withdrawals resumed, although the company stated this represented only about 2.1 percent of its reported assets.
| Metric | Details |
|---|---|
| Attack Date | October 29 |
| Assets Stolen | $6.3 billion - $6.43 billion |
| Binance Reimbursed | ~95% |
| Net Outflows Post-Resumption | ~$3.64 billion |
| Previous TraderTraitor Incidents | DMM Bitcoin attack ($308 million, 2024), Bitget ($387.5 million) |
AI Involvement and Past Incidents
Security experts cited in a Bloomberg report suggest that North Korean hackers might be employing artificial intelligence to plan and execute cryptocurrency thefts, pointing to the increasing complexity and precision of recent attacks, including the Binance heist. However, the use of AI has not been definitively confirmed.
TraderTraitor has a history of targeting crypto exchanges. The North Korean group has been previously linked to a string of cryptocurrency thefts, including the $308 million attack on Japan’s DMM Bitcoin exchange in 2024. The group has historically used deceptive tactics, such as fake job offers and recruitment exercises, to trick employees into granting access to their employers’ systems. This is not Binance’s first significant encounter with hackers; in 2022, attackers exploited its BNB blockchain bridge, making off with approximately $566 million in tokens.
This incident underscores the persistent and evolving threat landscape in the cryptocurrency sector, particularly from state-sponsored hacking groups. For users, it emphasizes the critical need for heightened vigilance and robust security practices. For crypto exchanges, it serves as a stark reminder to continuously fortify their security infrastructures, invest in advanced protective technologies, and maintain swift incident response plans to mitigate financial losses and uphold customer trust.
While it’s reassuring that Binance has reimbursed a significant portion of the stolen assets, the repeated success of groups like TraderTraitor raises serious questions about the fundamental security architecture of these exchanges. Attributing the theft to North Korea is one thing, but it doesn’t solve the underlying vulnerability that allowed a compromised laptop to grant such extensive access. How can users truly trust platforms when even billions in reserves can’t prevent such massive breaches, and the full recovery of niche tokens remains elusive?